The breach happened at Labcorp’s debt collector, American Medical Collection Agency, but now Labcorp is paying nearly $2.3 million to the states and agreeing to substantial changes in how it manages vendors receiving patient information.
What gives?
For covered entities that rely on business associates (and that would be pretty much all of them), this raises some uncomfortable questions. HHS has long said that HIPAA does not require covered entities to monitor how their business associates implement certain privacy safeguards. Business associates also have their own direct HIPAA obligations. So how exactly does the vendor’s breach become the covered entity’s settlement? And if the vendor caused the problem, how much of that settlement should it have to pay?
The Labcorp Settlement: Who Pays for What?
In September 2026, 44 attorneys general representing 43 states and the District of Columbia announced a settlement with Laboratory Corporation of America Holdings. It arose from the 2019 breach at Retrieval-Masters Creditors Bureau, which operated as American Medical Collection Agency, or AMCA.
As Delaware’s September 24 announcement explains, the breach potentially affected approximately 27.5 million people across AMCA’s customers, including approximately 10.2 million Labcorp patients. The larger number should not be attributed entirely to Labcorp.
Labcorp agreed to pay $2,287,455 across the participating jurisdictions. Publicly reported shares include Delaware’s $30,135, New York’s $89,178, Michigan’s $85,717, and New Jersey’s $68,000.
Labcorp’s obligations also extend beyond the payment. Michigan’s announcement describes requirements to strengthen information security and incident response, limit information shared with vendors, and improve vendor evaluation and oversight. Debt collector arrangements must address security standards, assessments, audits, and Labcorp’s ability to act when problems arise.
The Assurance of Voluntary Compliance sets an October 1, 2026 effective date, allows twelve months to amend existing debt collector contracts, and requires an independent assessment within eighteen months. Paragraphs 9 through 22 expire after five years, but that expiration does not apply to the entire agreement.
Notably, Labcorp did not admit liability. The agreement expressly disclaims any adjudication or finding of wrongdoing. These negotiated requirements also do not establish that a court would have required the same measures under existing law.
HIPAA or State Law? The Basis for AG Enforcement
The settlement agreement expressly covers HIPAA and state consumer protection, information security, and breach notification claims, so HIPAA was certainly part of the matter. However, Michigan filed its agreement under its Consumer Protection Act. The public agreements do not establish which alleged violations drove the payment, that every participating jurisdiction filed a federal HIPAA lawsuit, or how the payment was divided among the different legal theories. So the more accurate description is that this was a multistate data security settlement involving both HIPAA and state law, rather than a $2.3 million “HIPAA fine.”
Doesn’t HHS Say Covered Entities Don’t Have to Monitor Their BAs?
Yes. HHS’s published FAQ, “Is a covered entity liable for, or required to monitor, the actions of its business associates?”, explains that the Privacy Rule does not require covered entities to oversee how business associates implement privacy safeguards or comply with contractual privacy requirements. That guidance dates to 2002, before HITECH, and remains on HHS’s website.
But that FAQ does not answer every liability question. Its broader liability language needs to be read alongside the current Enforcement Rule. Covered entities also remain responsible for their own disclosures, compliance with the minimum necessary standard when applicable, and required business associate agreements (BAAs). Known problems require a response. Under 45 C.F.R. §164.504(e), knowledge of a business associate’s pattern or practice materially violating the agreement requires reasonable efforts to cure the breach or end the violation. If those efforts fail, termination is required when feasible. Signing a BAA does not excuse ignoring a material problem that later comes to light.
The Security Rule’s risk analysis and risk management duties also remain. HHS’s guidance calls for understanding where electronic PHI is created, received, maintained, and transmitted. Vendor arrangements belong in that assessment where relevant to the organization’s risks, although this does not establish a blanket duty to perform a full security audit of every vendor.
The current Enforcement Rule adds another consideration. Under 45 C.F.R. §160.402(c), covered entities can face civil monetary liability for HIPAA violations committed by business associates acting as their agents within the scope of that agency.
Agency depends on the relationship and federal common law principles, including the right to control the vendor’s conduct. An “independent contractor” label is not conclusive, and a BAA does not automatically establish agency. HHS discussed this distinction in its 2013 omnibus final rule.
A covered entity can therefore dispute an overbroad claim that HIPAA required it to supervise everything the vendor did, while still having to answer for its own conduct or violations committed by an agent. A vendor breach, standing alone, does not establish a covered entity violation. The factual questions that matter include:
- What information did the covered entity share?
- What risks did it identify?
- What did it know about the vendor’s problems, and how did it respond?
Those questions are more useful than assuming either that a BAA eliminates liability or that every vendor breach establishes a covered entity violation.
Did AMCA Get Away Withouth Paying?
Sort of. AMCA faced its own enforcement action. In March 2021, 41 attorneys general reached a separate settlement requiring security and compliance measures. However, the New York announcement describes a $21 million payment that was suspended because of AMCA’s financial condition, subject to the agreement’s terms. AMCA had filed for bankruptcy in June 2019 following the costs associated with responding to the breach. For covered entities negotiating indemnification, this is a huge practical concern. A vendor may promise to reimburse every expense but still lack the resources to pay. When many customers are affected, they may all be seeking recovery from the same insurance policy and remaining assets. The vendor’s ability to fund its promises deserves real attention before the contract is signed.
Does Your HIPAA BAA Actually Require the Vendor to Pay?
HIPAA does not require general indemnificaiton, and the HHS model HIPAA BAA’s reimbursement of breach notification costs does not cover every expense of an investigation or settlement. Because a settlement may leave fault unresolved, an indemnity requiring a final judgment establishing the vendor’s responsibility may offer little protection when the covered entity settles. The agreement should therefore allocate legally recoverable costs according to responsibility, address defense and settlement participation without giving the vendor an unreasonable veto, and expressly cover reasonable settlements reached under agreed procedures. It should also expressly address attorneys’ fees incurred enforcing the indmenity, otherwise the covered entity may have to fund another lawsuit just to recover what the vendor promised to pay.
If a vendor goes bankrupt after a breach, the covered entity may be left responding to regulators and paying expenses it expected the vendor to cover. The covered entity still has to answer for its own compliance under HIPAA and applicable state law, regardless of the vendor’s ability to pay. That is why the indemnity, insurance, and financial terms need attention before the PHI is shared with the vendor. Covered Entities should review the BAA alongside the services agreement, with particular attention to:
- The covered entity’s own losses. Provide for direct reimbursement as well as indemnification for third party claims. Address payment of defense expenses as incurred, including during an investigation before suit.
- Covered expenses. Include legal fees, forensic work, notification, call centers, appropriate credit monitoring, legally recoverable settlements and penalties, and reasonable corrective costs attributable to the vendor.
- Defense and settlement procedures. Establish notice, participation, counsel, consent deadlines, and remedies for failure to cooperate. Address reasonable settlements without making recovery dependent entirely on a final judgment.
- Shared responsibility. A “sole fault” requirement can obstruct recovery. Allocate costs according to each party’s contribution and address the vendor’s personnel and subcontractors.
- Caps and exclusions. Check whether another provision limits the indemnity to a few months of fees or excludes the very losses it appears to cover. Specify which document controls if the BAA and services agreement conflict, and which obligations survive termination. If each agreement says it overrides the other, fix that inconsistency before signing.
- Enforcement costs. Expressly cover fees incurred pursuing reimbursement and identify the dispute resolution process. A right to reimbursement can become expensive to exercise if the covered entity must absorb all the legal fees needed to enforce it.
- Financial backing. Examine appropriate insurance terms, limits, exclusions, and competing claims against the same coverage. Financial diligence or a parent entity guarantee may also be warranted. A certificate of insurance alone will not answer whether the policy covers the particular contractual obligation or expense at issue. A single large breach, especially one affecting multiple customers, can exhaust the policy’s available limits. The vendor may still owe you under the indemnity, but if it lacks the assets to pay or goes bankrupt, you may be left absorbing costs you expected the vendor’s insurance to cover.
Vendors will almost certainly push back on these terms. But before accepting a cap tied to a few months’ fees, compare that amount with what a serious breach could actually cost your organization! A low cap can leave the covered entity absorbing most of the expense, even when the vendor caused the breach. Remember, the breach happened at Labcorp’s debt collector, yet Labcorp still agreed to pay nearly $2.3 million and undertake substantial new compliance obligations. Indemnification cannot eliminate the covered entity’s own legal duties or prevent an investigation, but it can give the covered entity a contractual right to recover costs attributable to the vendor’s failures, but that protection depends on what the agreement actually covers and whether the vendor has the resources or insurance to pay.
Conclusion
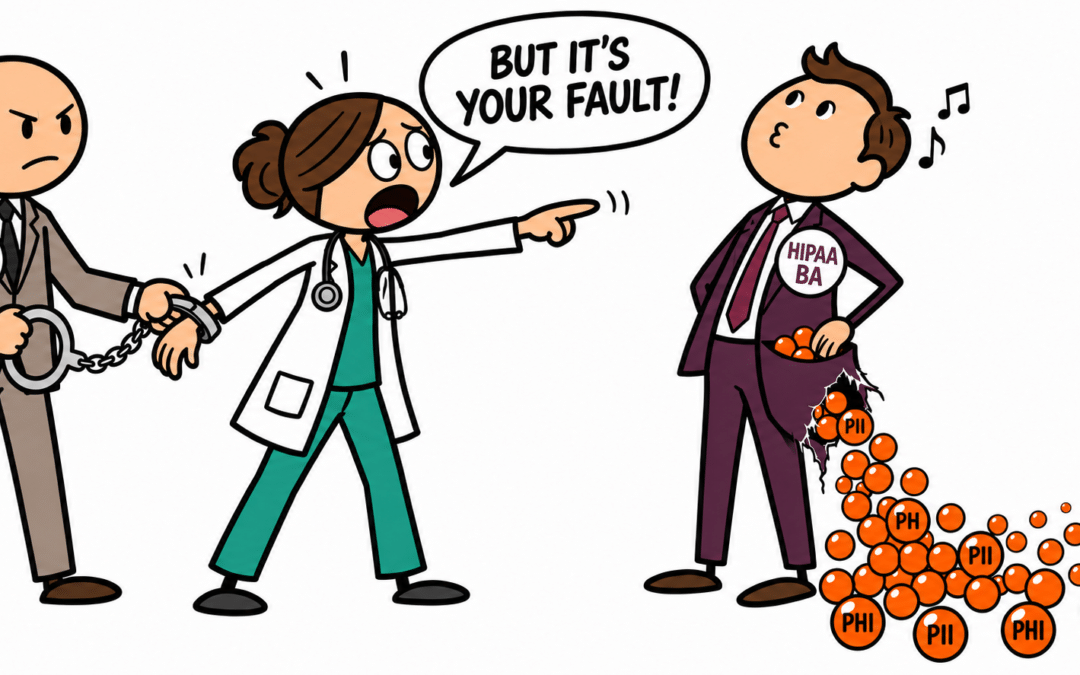
A business associate entrusted with patients’ PHI should accept meaningful financial responsibility for the harm its failures cause. If the vendor puts those PHI marbles into a pocket with a hole in it, the covered entity should not be left paying to pick them all up.