5 Reasons Why Your Training is Not Preventing HIPAA Violations by Employees

5 Reasons Why Your Training is Not Preventing HIPAA Violations by Employees

A State Court of Appeals recently reinstated a patient’s claim that an Indiana hospital is vicariously liable for the actions of its employee who shared the patient’s confidential information with an unauthorized third party.  Although the lower court originally dismissed the case, the appellate court found that there is a “genuine issue of fact” and remanded the case for further proceedings.  Now a potential monetary settlement teeters on the edge as the hospital’s potential liability for this employee’s HIPAA non-compliance rests in the hands of further proceedings in the lower court – so, you might want to ask why did this happen in the first place?

* HIPAA Training that is too basic and not focused on specific risk areas and organizational policies is not only non-compliant, but also largely ineffective. 

* HIPAA covered entities should have clear policies and training that address specific employee behaviors that are “high risk” for HIPAA violations. 

* Organizations must make sure they are training EVERYONE, and implementing effective Security Reminders.
read more
Will ONC’s Final Rule put HIEs between a “Block and a Hard Place”?

Will ONC’s Final Rule put HIEs between a “Block and a Hard Place”?

Under the ONC’s Final Rule on Information Blocking, Health Care Providers, HIEs and HINs will be legally prohibited from interfering with the access, exchange, or use of EHI unless an exception applies. However, HIEs/HINs that are HIPAA Business Associates are not allowed to use or further disclose PHI other than as permitted or required by their HIPAA BAAs with respective health care providers. So, what happens if a Health Care Provider and its HIPAA Business Associate HIE/HIN disagree on whether an exception allows EHI to be withheld from access, exchange or use under a certain set of specific facts?

read more
Don’t Make the Mistake of Over-Reporting Data Breaches Under HIPAA

Don’t Make the Mistake of Over-Reporting Data Breaches Under HIPAA

Evaluating incidents that affect protected health information (PHI) to determine whether they must be reported under HIPAA’s Breach Notification Rule is a delicate balancing act.  On the one hand, a HIPAA covered entity will want to avoid reporting an incident to the Secretary of HHS if it is not required to do so under the standards set forth in HIPAA’s Breach Notification Rule. On the other hand, a HIPAA covered entity that fails to report a HIPAA Breach risks being exposed to penalties from OCR for each day such Breach was not reported when it should have been. A recent Becker’s Health IT article brought attention to a Notice posted by Ann & Robert H. Lurie Children’s Hospital of Chicago

read more
ONC Delays Enforcement of the Information Blocking Certification Provisions of its CURES Act Final Rule for 3 months

ONC Delays Enforcement of the Information Blocking Certification Provisions of its CURES Act Final Rule for 3 months

Today, ONC announced that it will exercise its discretion in enforcing all new requirements under its Cures Act Final Rule which have compliance dates and time frames until 3 months after each such date identified in the Final Rule.  The ONC Final Rule is scheduled to be published on May 1, 2020 in the Federal Register.  The ONC has developed an “Enforcement Discretion Dates and Time frames” chart which indicates that the Part 170 Information Blocking provisions will have a compliance Enforcement Discretion Date of February 1, 2021.

read more
Summary List of COVID19-related Federal Actions Relevant to Healthcare

Summary List of COVID19-related Federal Actions Relevant to Healthcare

As efforts at the federal and individual states level evolve every day at almost a breakneck pace to address challenges and needs related to the COVID-19 outbreak, here is a running list of some of the top actions taken at the federal level that we thought would be helpful to the healthcare industry (Caveat, this is not an exhaustive list):  [updated: July, 28, 2021]

read more
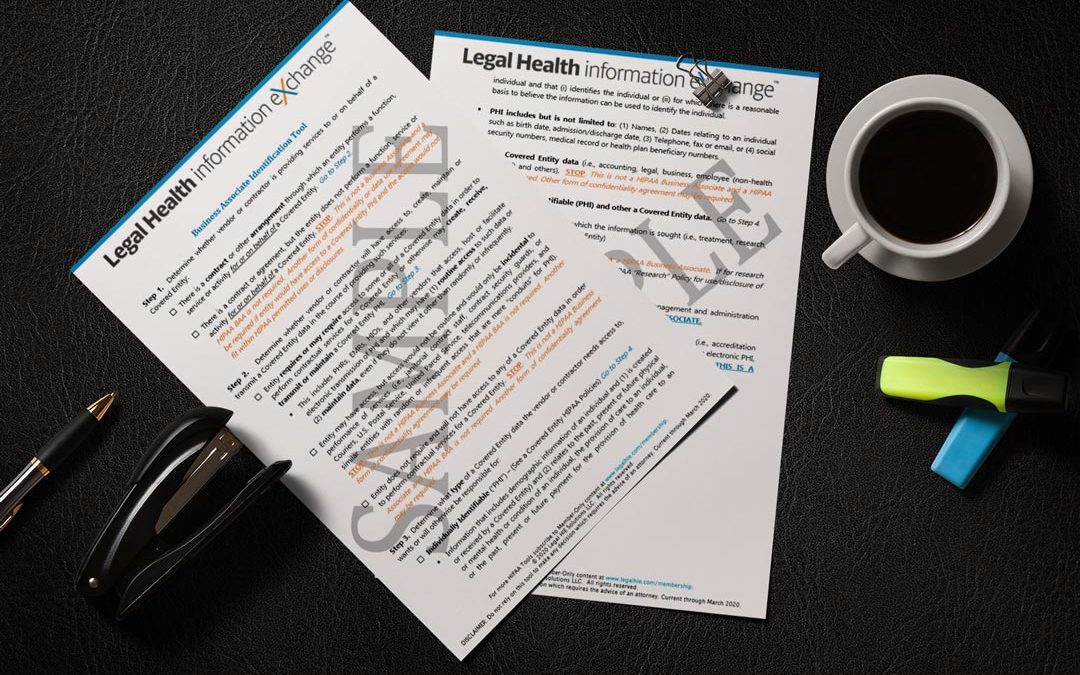
Do I Need a HIPAA Business Associate Agreement?

Do I Need a HIPAA Business Associate Agreement?

A HIPAA “Business Associate” is a person, other than a member of the workforce, who creates, receives, maintains or transmits PHI in the performance of services or functions for or on behalf of a Covered Entity. Treatment and Payment disclosures do NOT create a HIPAA BA relationship. Conduits are not HIPAA BAs, but the exception is very narrow. Covered Entities should review each HIPAA BA Agreement is needed, or not.

read more
“Top 10” List for Security Law Compliance

“Top 10” List for Security Law Compliance

“Top 10” List for Security Law Compliance As we bid farewell to late night comedy host David Letterman, I thought it appropriate and timely to give a nod to one of Letterman’s most iconic segments, his “Top 10”, with my own Top 10 list for complying with applicable Security Law: #10.  THE HIPAA...

read more

Archives